

Cyber Essentials Funded Programme: Government Support for UK SME's
Helping UK SMEs Strengthen Cyber Defences with Government Support
In today’s digital-first world, cyber threats are no longer a distant concern – they’re a daily reality. The UK government’s Cyber Essentials scheme offers a practical, affordable way for organisations to defend against the most common attacks.
Whether you’re a small business or a growing tech innovator, this funded programme helps you build a strong security foundation, earn customer trust, and unlock new opportunities – including eligibility for government contracts. And with CyberLab’s expert guidance, getting certified is simpler than ever.
What is Cyber Essentials?
Cyber Essentials is a government-backed initiative to help businesses protect against the most common cyber threats. Originally launched in 2014, over 120,000 certificates have since been awarded to businesses of all sizes across the country.
According to the UK government, obtaining Cyber Essentials certification protects your organisation from approximately 80% of cyber-attacks, demonstrating a strong commitment to cyber security and data protection to customers and stakeholders. This certification enhances your organisation’s reputation, increases the likelihood of securing new business, and enables you to bid for and win UK government contracts. By ensuring that robust cyber security measures are in place, Cyber Essentials provides the peace of mind needed to focus on your core business objectives.
Cyber Essentials Plus
Cyber Essentials Plus is the next step in your cyber security journey – an advanced government-backed initiative for businesses looking to take extra measures to protect against common cyber threats.
Around a quarter of businesses who take the Cyber Essentials certification go on to achieve Cyber Essentials Plus.
What is the funded Cyber Essentials Programme?
Every business today faces the risk of a cyber attack, but some organisations are particularly vulnerable. This could be because they handle sensitive information about the people they work with or are seen as easier targets by cyber criminals.
To help those most at risk, the NCSC is rolling out a Funded Cyber Essentials Programme. This programme is aimed at supporting vulnerable organisations by helping them implement basic security measures to protect against the most common types of cyber attacks.
How Does it Work?
The programme offers practical support from an Advisor to help your organisation achieve Cyber Essentials Plus, at no cost to the organisation. However, if the Advisor recommends any extra software or hardware, those costs won’t be covered.
If you qualify, you’ll get around 20 hours of remote support with an Advisor. They’ll spend this time working with you to identify and implement improvements that suit your organisation’s size and needs, guiding you through the five Cyber Essentials technical controls. After that, there will be a hands-on technical check to make sure everything is in place.
If it turns out that achieving Cyber Essentials Plus isn’t possible, the Advisor will help you implement as many of the controls as you can and provide a clear list of what else needs to be done to get compliant. This scheme is designed to walk you through the technical controls required for Cyber Essentials certification, leading up to the Cyber Essentials Plus audit. No previous cybersecurity certification or experience is needed.
Who is Eligible for Support?
To qualify for this scheme, companies must be a micro or small business (1 to 49 employees) registered in the UK and working on:
- The development of fundamental Artificial Intelligence (AI) technologies, OR the innovative application of Artificial Intelligence technologies in the following sectors: Public safety and health, Defence and security.
- The development of novel Quantum technologies.
- The design, development or manufacturing of semiconductors / semiconductor IP blocks.
- The development of Engineering Biology or Synthetic Biology.
AND meet the following criteria:
- Has not previously participated in the NCSC Funded Cyber Essentials Programme
- Does not currently hold Cyber Essentials Plus (CE+) certification, has not been awarded CE+ certification since January 2023 and is not currently in the process of applying for CE+ certification
How CyberLab Can Help
As an IASME approved assessor, CyberLab is not only authorised to assess against the scheme, but also able to support your organisation to achieve certification.
Not only are we authorised Cyber Essentials assessors, we are also able to provide bespoke consultancy services to assist your team in meeting and maintaining the high standard of security required.
With our expert advice, you’ll pass first time.

Understanding the Digital Operational Resilience Act (DORA)
A Guide for UK Businesses
The Digital Operational Resilience Act (DORA) is a landmark regulation introduced by the European Union (EU) to bolster the cyber security and operational resilience of the financial sector.
Despite DORA coming into effect as of 17th January 2025, little is still known about the new regulation and who it applies to. In this blog we cover what UK businesses and organisations need to know about DORA, its implications, and how to prepare.
What is DORA?
DORA is an EU regulation that aims to ensure financial institutions, and their critical ICT (Information and Communications Technology) providers can withstand, respond to, and recover from ICT-related disruptions.
It establishes uniform requirements for managing ICT risks, operational resilience, and incident reporting across the EU financial sector.
Key components of DORA include:
- ICT risk management frameworks
- Comprehensive incident reporting mechanisms
- Regular operational resilience testing
Oversight of third-party ICT providers For more details, visit the European Insurance and Occupational Pensions Authority (EIOPA) for an overview of DORA.
Who Does DORA Apply to?
DORA applies to a wide range of financial entities and their critical third-party ICT service providers operating in the EU. These include:
- Banks, payment service providers, and investment firms.
- Insurance and reinsurance companies.
- Cryptocurrency service providers.
- Critical third-party ICT providers offering services like cloud computing, data analytics, and cyber security solutions.
For UK-based businesses, DORA applies if:
- You provide financial services or ICT solutions to EU-based clients.
- You are a critical ICT service provider for EU financial institutions.
What Does DORA Mean for UK Businesses and Organisations?
DORA Penalties for Non-Compliance
Guidance and Recommendations for Businesses and Organisations Affected by DORA
Conclusion
CyberLab joins the Cyber and Fraud Centre – Scotland: Protecting Scottish Businesses
New Membership Helping Scottish Businesses Strengthen Cyber Resilience
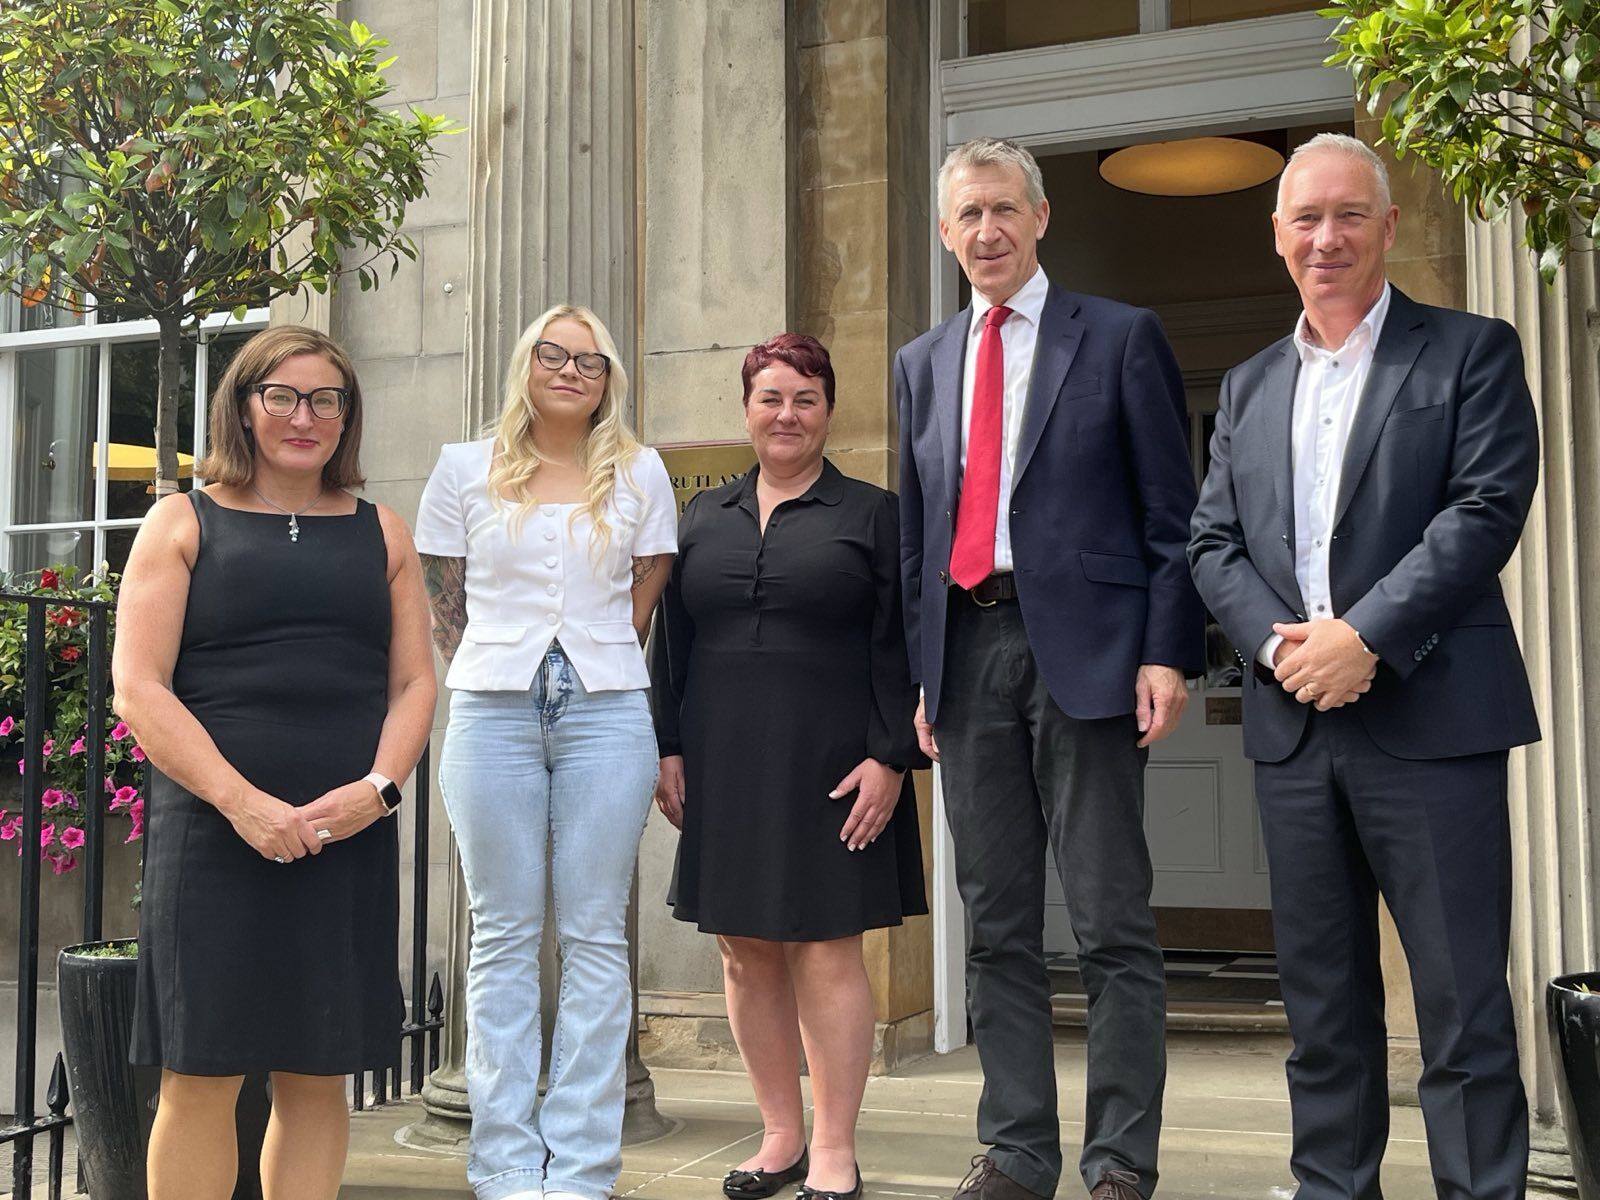
CyberLab is proud to join the Cyber and Fraud Centre Scotland, strengthening our commitment to helping businesses stay secure through expanded community outreach.
The Cyber and Fraud Centre – Scotland is a leading organisation dedicated to equipping businesses with the knowledge and resources needed to combat cyber threats and fraud.
The Centre plays a critical role in supporting businesses, charities, and social enterprises by providing expert-led training, practical advice, and access to essential security resources. Its unique partnerships with Police Scotland and the Scottish Government place the Centre at the forefront of national cyber security and fraud prevention efforts.
“We’re thrilled to join forces with the Cyber and Fraud Centre – Scotland to support businesses and organisations in becoming more secure and resilient. The Centre’s socially driven mission and partnerships with key national bodies align perfectly with our commitment to building a safer digital future.
As cyber threats evolve, collaboration is essential. Together, we aim to provide businesses with the tools and knowledge needed to navigate today’s complex security landscape.”
– Wayne Price, Commercial Director at CyberLab
Through this membership, CyberLab will collaborate closely with the Centre to enhance its security offerings, benefiting from expert insights and tailored training programmes. These initiatives will empower businesses of all sizes to strengthen their defences, reduce risks, and build long-term resilience against cyber and fraud-related threats.
“We’re delighted to have CyberLab join the Scottish Cyber Security Network. Their experience and dedication to improving the cyber security landsdcape in Scotland will be a real asset to our membership community.
Collaborating with members like CyberLab strengthens our shared efforts to enhance Scotland’s cyber resilience, and we’re excited about the contributions they’ll bring to the network.”
As cyber threats evolve, collaboration is essential. Together, we aim to provide businesses with the tools and knowledge needed to navigate today’s complex security landscape.”
– Jude McCorry, CEO at Cyber and Fraud Centre Scotland
About CyberLab
CyberLab is a specialist cyber security company that provides a wide range of security solutions and services.
Your one-stop cyber security advisor, the CyberLab team is equipped with the right technology, knowledge, and expertise to help businesses of all sizes, including large public sector organisations.
By leveraging world-class technology, decades of experience, and their extensive vendor partnerships, CyberLab have helped to secure thousands of organisations across the UK.
About The Cyber and Fraud Centre Scotland
The Cyber and Fraud Centre – Scotland is a leading and trusted provider of cyber services, training, and advice. Its team is dedicated to protecting organisations across Scotland. As a social enterprise, the Centre stands apart from other cyber support providers by reinvesting in the cyber community. This ensures that every business, charity, membership body, or social housing organisation it supports – regardless of size or structure – has access to essential security resources.
By combining expert knowledge with a socially driven mission, the Centre is reshaping how cyber support is delivered, fostering trust, collaboration, and a shared commitment to a safer digital future.
Why Windows 10’s End of Life Matters for Cyber Essentials Plus
Navigating Compliance After Microsoft Ends Support for Windows 10
Microsoft officially ended support for Windows 10 on 14 October 2025, marking a major shift for organisations working toward Cyber Essentials Plus (CE+) certification. Without free security updates or patches, Windows 10 devices now pose a compliance risk – unless covered by Microsoft’s Extended Security Updates (ESU) programme.
For CE+ applicants, this change is more than a technical footnote. It directly affects your certification status. Devices running Windows 10 are no longer considered secure by default. To remain compliant, organisations must upgrade to Windows 11 version 23H2 or newer (ideally 24H2 or 25H2).
If your CE+ audit is scheduled within the 90-day window following your Cyber Essentials certification, any Windows 10 devices must be upgraded or removed from scope before submitting your asset list to the auditor.
“With Windows 10 now out of support, organisations pursuing Cyber Essentials Plus must act quickly. Upgrading to Windows 11 isn’t just best practice – it’s essential for compliance. At CyberLab, we’re here to make that transition smooth, secure, and audit-ready.”
– Ryan Bradbury, CTO at CyberLab
Why It Matters
Auditors will now perform technical verification during CE+ assessments.
If Windows 10 devices are detected:
- They must be excluded from scope.
- Failure to do so could result in audit failure or the need to restart both Cyber Essentials and CE+ assessments.
What You Need to Do Now
To stay secure and compliant, here are your next steps:
- Audit your device inventory: Identify any machines still running Windows 10.
- Upgrade to Windows 11: Preferably version 24H2 or 25H2. Note that 23H2 reaches end of life on 11 November 2025, so plan accordingly.
- Consider ESU: If upgrading isn’t feasible, explore Microsoft’s Extended Security Updates programme.
- Communicate with your auditor: Be transparent about your upgrade plans and ensure your asset list reflects only compliant devices.
This transition is a critical moment for organisations aiming to maintain Cyber Essentials Plus certification. By acting now, you’ll avoid last-minute surprises and ensure your systems meet the latest security standards.
Need help navigating the upgrade or preparing for your CE+ audit? CyberLab’s team is here to support you.
Understanding Incident Management: Your Cyber Safety Net
Incident Response Essentials for Every Team
What is Incident Response?
Tales from the CyberLab: Ransomware Response Explained
Incident Response Retainers: Are They Really Necessary?
Fail to Prepare; Prepare to Fail
Conclusion
Protecting Automotive Manufacturing from Cyber Threats
A Futaba Manufacturing Success Story
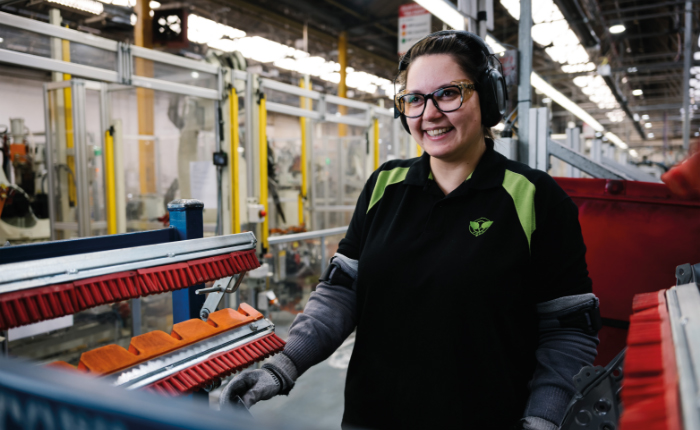
The automotive industry is built on precision, efficiency, and reliability. However, as manufacturing processes become more interconnected and reliant on digital systems, the risk of cyber threats continues to grow. A single cyber attack can lead to production downtime, supply chain disruptions, and reputational damage – posing significant risks to operational continuity.
The Challenge: Securing Critical Manufacturing Operations
As a leading supplier of automotive parts, Futaba Manufacturing UK (FMUK) faced growing concerns about cyber threats targeting their critical manufacturing operations. With an expanding network of IoT devices, a single cyber attack could bring production to a halt, causing financial loss and reputation damage. Futaba needed a robust cyber security solution to safeguard sensitive data, ensure operational continuity, and protect their valuable intellectual property.
The Growing Cyber Threat Landscape
Manufacturing businesses are increasingly vulnerable to cyber threats such as ransomware and data breaches, with cyber criminals targeting industrial control systems, supply chains, and sensitive data. According to recent industry reports, manufacturers have become prime targets for cyber-attacks, and a significant breach could compromise production lines, erode customer trust, and lead to significant financial repercussions.
According to the Sophos State of Ransomware in Manufacturing and Production 2024 report, 65% of manufacturing and production organisations were hit by ransomware last year – a sharp rise from 56% in 2023 and 55% in 2022, marking a 41% increase since 2020.
Futaba Manufacturing, with its critical role in the automotive sector, understood that protecting their operations against cyber threats was a necessity – not just a priority. To safeguard their systems and future-proof their operations, they turned to CyberLab for a comprehensive and tailored cyber security solution.
Identifying Vulnerabilities and Securing Operations
CyberLab’s first step was to conduct an in-depth penetration test, beginning with an assessment of Futaba’s external infrastructure. This process uncovered potential vulnerabilities in their network and critical systems. By simulating real-world attack scenarios, CyberLab identified the risks that could be exploited by cyber criminals looking to disrupt manufacturing processes.
A Multi-Layered Security Approach
To combat evolving threats, CyberLab implemented a multi-layered security strategy for Futaba Manufacturing, with advanced detection systems, robust access control, and proactive monitoring.
The strategy included:
- Sophos Managed Detection & Response (MDR): This 24/7 monitoring service helped Futaba detect and mitigate threats in real time, giving their IT team the ability to focus on high-priority tasks while CyberLab’s experts managed their security operations.
- IoT Device Security: Given the increasing use of connected devices in Futaba’s manufacturing processes, CyberLab placed special focus on securing their IoT infrastructure, ensuring that all endpoints were protected from potential vulnerabilities.
Strengthening Internal Defences and Employee Awareness
A major part of Futaba’s defence strategy involved strengthening internal security. CyberLab conducted user awareness training across the company to ensure that employees were aware of phishing scams and social engineering tactics. By fostering a culture of security, Futaba empowered its staff to act as the first line of defence against cyber threats.
Additionally, CyberLab deployed advanced endpoint protection and email security to minimise the risk of malware or phishing entering the organisation through vulnerable communication channels.
The Results: Securing the Manufacturing Future
The implementation of CyberLab’s security solutions has significantly strengthened Futaba Manufacturing’s cyber resilience. With 24/7 threat monitoring, advanced IoT security, and comprehensive training for employees, the risk of cyber incidents and production downtime has been drastically reduced.
As a result, Futaba can now operate with confidence, knowing that their systems, data, and intellectual property are protected. The company’s commitment to proactive security enables them to stay ahead of cyber threats while maintaining a reputation as a reliable partner within the automotive industry.
A Trusted Cyber Security Partnership
Futaba’s partnership with CyberLab allowed them to take a proactive approach to cyber security, with continuous support and tailored consultancy. The collaborative relationship ensured that Futaba could keep their defences up-to-date and adapt quickly to emerging threats in the rapidly evolving cyber landscape.
Conclusion: Embracing a Secure Future for Manufacturing
Futaba Manufacturing’s collaboration with CyberLab has provided them with the tools and expertise needed to navigate the increasingly complex cyber threat landscape. With a strong cyber security framework in place, Futaba is well-positioned to grow while ensuring operational continuity and protecting sensitive data.
As manufacturing businesses continue to face heightened cyber risks, it’s crucial for companies like Futaba to adopt a proactive, multi-layered security strategy. The success of this partnership serves as a powerful reminder of how robust cyber security measures can protect against evolving threats, ensuring that businesses can thrive in an interconnected, digital world.
Protecting E-Commerce Operations from Cyber Threats
A Sealey Tools Success Story
E-commerce has become the backbone of modern retail, offering convenience and accessibility to customers worldwide.
However, with this digital shift comes an increasing risk of cyber threats that can compromise business continuity, customer trust, and financial security. For Sealey Group, a leading provider of professional tools and workshop equipment, safeguarding their online operations was not just a priority – it was a necessity.
The Growing Cyber Threat Landscape
Cyber threats such as ransomware and phishing attacks have become a persistent challenge for online retailers. According to the Sophos State of Ransomware Report 2024, 45% of omnichannel retailers faced ransomware attacks last year alone. These threats put businesses at risk of data breaches, operational downtime, and reputational damage.
As a company with over 13,000 product lines and a strong e-commerce presence, Sealey Group required a robust cyber security strategy to ensure their platform and payment systems remained secure. A single cyber attack could disrupt sales, erode customer confidence, and result in financial losses. To fortify their defences, Sealey Group turned to CyberLab for a comprehensive cyber security solution.
Identifying the Vulnerabilities
CyberLab’s first step was to conduct a thorough penetration test, beginning with an external infrastructure assessment. This process would help uncover vulnerabilities in Sealey Group’s publicly accessible systems. To simulate real-world attack scenarios, an on-site assessment was also performed within their corporate network. These evaluations provided critical insights into potential weaknesses that cyber criminals could exploit.
A Multi-Layered Security Approach
Understanding the sophistication of modern cyber threats, CyberLab implemented a layered security strategy to reinforce Sealey Group’s resilience. This strategy included advanced threat detection, robust email security, and endpoint defences, ensuring that multiple barriers were in place against potential attacks.
One of the key components of the security framework was Sophos Managed Detection & Response (MDR), which offered 24/7 expert-led threat hunting. This proactive approach allowed CyberLab’s security analysts to identify and neutralise threats before they could cause harm. Sophos MDR’s automation capabilities handled most security incidents, enabling analysts to focus on detecting more advanced, stealthy attacks.
Strengthening Email Security and Data Protection
Email remains one of the most common entry points for cyber threats, making it crucial for Sealey Group to strengthen their defences. In collaboration with Mimecast, CyberLab implemented an advanced email security system that protected both internal and external communications. This measure provided targeted threat protection and rapid remediation against phishing attempts and other email-based attacks.
To further enhance data protection, a Microsoft Teams archive was introduced to securely store customer information. Additionally, a secure file-sharing service and 24/7 telephone support were integrated to ensure seamless communication and business continuity.
A Trusted Cyber Security Partnership
Sealey Group’s long-standing partnership with CyberLab played a vital role in tailoring the security solutions to their specific needs. Through dedicated account management and expert consultancy, CyberLab provided a proactive approach to cyber security, ensuring Sealey Group remained ahead of emerging threats.
The Results: A Resilient E-Commerce Platform
The implementation of CyberLab’s security measures has significantly bolstered Sealey Group’s cyber defences. With round-the-clock threat monitoring and advanced email protection, the risk of downtime and data breaches has been drastically reduced. This has not only safeguarded customer trust but also ensured the smooth operation of Sealey Group’s omnichannel business.
By adopting a proactive approach to cyber security, Sealey Group has set a strong foundation for continued growth and operational integrity. Their commitment to resilience serves as a testament to how businesses can thrive in an evolving cyber landscape when equipped with the right defences.
Conclusion: Navigating the Digital Future with Confidence
For over six years, Sealey Group and CyberLab have worked together to navigate the complex and ever-changing world of cyber security. This partnership has ensured that Sealey Group remains well-equipped to counter emerging threats, maintain business continuity, and uphold its reputation as a trusted retailer.
As cyber threats continue to evolve, businesses must remain vigilant and proactive in their security strategies. Sealey Group’s success story highlights the importance of a comprehensive cyber security framework, demonstrating that with the right measures in place, businesses can confidently operate in the digital landscape, secure in the knowledge that their operations and customer data are protected.
Chess Acquires CyberLab: Building a Cyber Security Powerhouse
Chess and CyberLab: Building a Cyber Security Powerhouse
Chess Cyber Security and CyberLab have combined forces to deliver one of the most comprehensive cyber security offerings in the UK.
This strategic integration brings together deep technical expertise, innovative technology, and a proven track record of helping organisations manage risk and strengthen resilience.
Why This Matters for Customers
Cyber threats continue to evolve, and businesses need partners who can provide end-to-end protection – from assessment and testing to consultancy, implementation and ongoing management.
By joining Chess, CyberLab enhances this capability, creating a single point of access for:
- Testing and assurance: Penetration testing, vulnerability assessments, and compliance audits
- Managed security services: Continuous monitoring, threat detection and response
- Governance and certification: Cyber Essentials, Cyber Essentials Plus and IASME Cyber Assurance
- Security-as-a-Service (CSaaS): A holistic platform that combines consultancy, technology and training to simplify cyber risk management
What CyberLab Brings to the Table
CyberLab introduced an innovative security-as-a-service model, giving organisations a centralised portal to:
- View and manage their security posture
- Identify individual blind spots
- Automate fixes with tailored training programmes
- Access compliance frameworks and reporting in one place
This approach makes cyber security simpler, more transparent and more actionable for businesses of all sizes.
A Track Record of Excellence
Chess has long been recognised as a trusted technology partner, with awards including:
- Sophos Public Sector Partner of the Year (10+ years)
- Sophos Mid-Market Partner of the Year
- Forescout Commercial Partner of the Year
- Consistently ranked in the Top 100 Companies to Work For
The integration of CyberLab builds on previous milestones, such as the acquisition of Armadillo Sec and Foursys, reinforcing Chess’s position as a leader in cyber security.
What This Means for You
Today, customers benefit from:
- Comprehensive coverage: From discovery and testing to consultancy and managed services
- Expertise at scale: CREST-accredited penetration testers, certified consultants and award-winning partners
- Simplified management: A single portal for posture assessment, compliance and training
- Future-ready security: Solutions designed for hybrid work, cloud adoption and evolving threat landscapes
Looking Ahead
Cyber security is critical for every organisation.
By combining Chess’s breadth of services with CyberLab’s specialist capabilities, we provide the agility, insight and technology needed to protect businesses now and in the future.
CyberLab Celebrates Recognition in Top 100 Best Companies 2025
CyberLab Celebrates Three Top 10 Results in Best Companies 2025
🏆 #8 Best Small Company To Work For in the UK
🏆 #10 Best Company to Work For in the North West
🏆 #5 Best Company to Work For in the Technology Sector
CyberLab is proud to celebrate our latest recognition in the prestigious Best Companies™ 2025 rankings!
These outstanding achievements are a testament to the incredible people who make CyberLab what it is. Their passion, creativity, and commitment to building a culture of excellence continue to drive us forward.
A Message from CEO Gavin Wood
“I’m incredibly proud to announce that once again we’ve delivered a fantastic result in this year’s Best Companies survey, and this time we’ve improved on last year’s performance.
What makes this achievement meaningful is the collective effort behind it. From our people helping our customers defend against the evolving cyber security threat landscape, to our leadership team shaping culture and direction, every person has played their part.
Our focus on Simplicity, Passion and Quality continues to pay off. This advance isn’t just a number or a badge. It’s a signal that our commitment to being a great place to work, and a great partner for our customers, is working.
As we grow, evolve and tackle new challenges, maintaining our culture is just as important as hitting targets. A big thank you to the whole team. Let’s build on this momentum and make next year even stronger.”
“I am over the moon to announce our results for Best Companies 2025. These incredible results are a testament to our people, plus their hard work and dedication in making CyberLab a great place to work.”
– Mimi Rostron, People & Culture Manager
At CyberLab, we believe that prioritising the wellbeing of our people is essential to both personal and organisational growth.
In this milestone year, we extend our heartfelt thanks to our incredible team. Their passion and commitment make this recognition possible, and we look forward to building on this success together.
Top 5 Cyber Security Predictions for 2026 and How to Prepare Now
Expert Insights from the CyberLab Board
In November 2025, the UK Government released a comprehensive report on the economic cost of cyber crime, which highlights how the average cyber incident costs a UK business £195,000. Scaling this to an annual UK cost, generates an estimate of £14.7 billion, equivalent to 0.5% of the UK’s GDP [Source]. The growing threat landscape and significant cost of cyber crime makes cyber security a pressing issue for all UK businesess.
2026 is set to be a landmark year for cyber security. AI, deepfake technology, quantum risk and supply chain vulnerabilities are converging to reshape the cyber landscape. Cyber criminals are now faster, more scalable and increasingly autonomous, relying less on human expertise and more on intelligent, self-learning tools.
In response, cyber defence must evolve too. It is no longer enough to react. Security needs to be predictive, adaptive and capable of operating at machine speed.
CyberLab’s Board have put together their predictions for 2026, and their insights reveal powerful themes that businesses must prepare for.
1. AI Changing the Threat Landscape: Defence and Attack at Machine Speed
AI is not just changing cyber security. It is redefining it. In 2026, AI will accelerate cyber defence, enabling faster detection, automated response and real-time threat modelling. However, it is also lowering the barrier to entry for cyber criminals, powering attack strategies that are faster, continuous and increasingly self-managing.
David Pollock, Chairman, highlights this duality:
“AI will speed up hackers’ ability to attack businesses and government. AI will also speed up our ability to defend and protect our customers.”
We will see a shift from human-led attacks to AI-led adversaries capable of executing cyber attacks without direct human involvement. These systems will operate at machine speed, identifying vulnerabilities, exploiting zero-day flaws and coordinating simultaneous attacks across multiple networks.
AI-driven attacks will be able to adapt mid-attack, changing strategies in response to defensive actions. They will learn from failed attempts, replicate successful exploits and scale attacks globally in seconds.
Ryan Bradbury, CTO, explains:
“The speed, scale and automation possible with agent-driven attacks will surpass anything we’ve seen before. We have to stop preparing only for human-led threats and start planning for autonomous AI-led adversaries.”
This means cyber defence will need to become dynamic, adaptive and automated. Continuous validation, predictive analytics and machine-speed response will become non-negotiable. AI-led defence will become the standard, not the exception.
2. Deepfakes, Identity Fraud and the Human Factor
While AI transforms the technical threats, humans will remain the most vulnerable target. In 2026, social engineering will become significantly more sophisticated as deepfake technology enables hyper-realistic voice, video and identity spoofing.
Wayne Price, Commercial Director, warns:
“Deepfakes and synthetic media will cause a surge in identity fraud, forcing organisations to ramp up digital identity verification practices.”
Attacks will no longer rely on poorly written phishing emails. Instead, employees may receive video messages from a supposed CEO requesting payment transfers, or voice calls mimicking trusted suppliers.
Gavin Wood, CEO, believes identity protection and human awareness will be critical:
“Human attack vectors will continue to be exploited, especially with AI-driven deepfakes, voice spoofing, phishing, and super realistic, authentic-looking videos, et cetera. Securing the human will be absolutely key for cyber security in 2026.”
Identity and access management will become one of the most important areas of cyber security, with organisations investing heavily in digital identity verification, behavioural biometrics and continuous trust authentication.
3. The Future of Ransomware and Smarter Phishing
Ransomware will remain one of the biggest threats in 2026, but AI will make it more intelligent, harder to detect and significantly more scalable. Attackers will use AI to craft personalised phishing emails that are context-aware and perfectly mimic internal communications or supplier messages.
Adam Myers, Sales Director, has seen a clear rise in this trend:
“We’re seeing emails that look more real and on brand. It’s harder to spot. AI is helping hit that on scale.”
These emails are technically perfect, grammatically accurate and contextually relevant, making them almost indistinguishable from legitimate communications. AI will also be used to test email variations, conducting A/B testing on targets to improve success rates.
Elena Doncheva, Marketing Director, advises:
“Train your people, as they will likely be the first line of defence. Monitor your digital footprint and the dark web for data that attackers can utilise. Test your business continuity plans, disaster recovery and incident response plans. You can never be too prepared.”
4. Quantum Risk, IoT Growth and Zero Trust Security
5. Supply Chain Security Becomes a Business Requirement
Final Thoughts: Secure Your Organisation and Use Cyber Security as Competitive Advantage