What is an IT Health Check?
An IT Health Check (ITHC) is a structured series of controlled security tests designed to identify vulnerabilities in an organisation’s IT infrastructure, systems and applications. It is the mandated form of penetration testing for public sector organisations in the UK, required before connecting to government networks and approved data-sharing environments.
ITHCs are delivered exclusively by suppliers accredited under the CHECK scheme, which is administered by the National Cyber Security Centre (NCSC). CHECK-accredited suppliers are security-cleared, making them the only approved providers for testing public sector systems. CyberLab is a CHECK-accredited provider, with a team of CHECK Team Leaders (CTLs) and CHECK Team Members (CTMs) experienced in delivering ITHCs across central government, local authorities, the NHS and regulated industries.
When is an IT Health Check Required?
An ITHC is mandatory in a number of specific situations. Organisations must complete an ITHC before connecting to the Public Services Network (PSN), before being listed on G-Cloud, before achieving NHS Digital Security Protection Toolkit (DSPT) compliance, and before connecting to the Pensions Dashboards Programme (PDP) ecosystem.
Some regulated industries and procurement frameworks also require evidence of a current ITHC as part of supplier due diligence. If your organisation is subject to any of these requirements, CyberLab can scope and deliver your ITHC to meet the specific code of connection requirements for each framework.
Why an IT Health Check?
An IT Health Check goes beyond a standard vulnerability scan. It provides a structured, methodical assessment of your entire IT environment – from external infrastructure and internal systems to applications, APIs and remote access – giving your organisation a clear, evidenced picture of its security posture and a prioritised remediation plan.
For public sector organisations, an ITHC is not optional. It is a prerequisite for connecting to government-approved networks and data-sharing frameworks, and the results feed directly into your compliance and audit reporting. Getting it right first time matters – and that starts with choosing a CHECK-accredited provider with genuine public sector experience.
Why Choose CyberLab for an IT Health Check?
CHECK Team Leaders on Every Engagement
Every CyberLab ITHC is led by a CHECK Team Leader (CTL) - not a junior tester working toward certification. Our team includes 7 CTLs and 6 CTMs, all SC or NPPV3-cleared and experienced in delivering ITHCs across central government, the NHS and regulated industries.
SC and NPPV3-Cleared Consultants
Our testers hold the security clearances required to access and test sensitive public sector systems. This is a mandatory requirement for CHECK-scheme testing - and a non-negotiable one for organisations whose systems handle government or classified data.
PSN, G-Cloud, NHS DSPT and PDP Expertise
We have direct experience delivering ITHCs to meet the specific code of connection requirements for each framework - so your report is formatted correctly, your scope is defined accurately and your submission is audit-ready first time.
Next-Day Testing Available
Compliance deadlines, audit requirements and connection windows don't always allow for lengthy lead times. CyberLab offers next-day testing for urgent ITHC requirements - speak with our team to discuss your timeline.
Audit-Ready Reporting
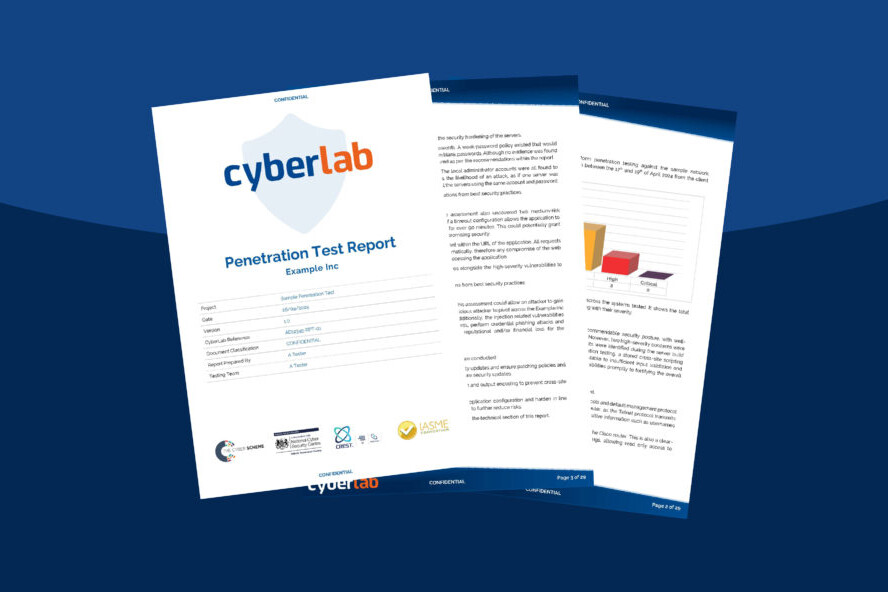
Every ITHC report is structured to meet the submission requirements of the relevant framework - PSN, G-Cloud, NHS DSPT or PDP - with CVSS-scored findings, remediation guidance and an executive summary for leadership and auditors.
No Jargon, No Orphaned Reports
We don't hand over a PDF and disappear. Our consultants are available to walk you through findings, support remediation planning and confirm scope for re-testing where required.
IT Health Check: The CyberLab Approach
1 Planning and Scoping
One of our CHECK Team Leaders will work with you to define the scope of the engagement, establish rules of engagement, and confirm which environments, assets and systems are in scope. For organisations connecting to the Pensions Dashboards Programme, scope must include any environment where live pension data will be used - including external infrastructure, internal systems, applications, APIs and remote access services. We will help you define this clearly before testing begins to avoid gaps in your submission report.
2 External Testing
Our team assesses all internet-facing systems and assets that store, process or transmit sensitive data. This includes reviewing data security configurations, TLS implementations, firewall rules and network segmentation, and testing against OWASP Top 10 vulnerabilities. Automated and manual vulnerability scanning is conducted to identify external attack vectors.
3 Internal Testing
Internal testing covers all in-scope assets including servers, databases, file systems and internal network infrastructure. We assess database security configurations, server and network hardening, internal firewall and security gateway configurations, wireless setups where applicable, and access controls including VPN and third-party access. Least privilege access enforcement is reviewed across all relevant environments.
4 Vulnerability Scanning
Automated and manual vulnerability scanning is conducted across both external and internal environments. Findings are classified by criticality and CVSS score (version 3.0 or above), in line with NCSC and PDP reporting requirements.
Our Accreditations
As a CHECK and NCSC-accredited IT Health Check provider, trusted by 1,200+ organisations including NHS Trusts, local authorities and central government bodies, we’ve delivered 14,000 hours of security testing – with SC-cleared CHECK Team Leaders available from the next working day.
What Does an IT Health Check Cover?
1 External Infrastructure
All internet-facing systems and assets that store, process or transmit sensitive data - including data security configurations, TLS implementations, firewall rules and network segmentation. Tested against OWASP Top 10 vulnerabilities using both automated and manual techniques.
2 Internal Infrastructure
Servers, databases, file systems and internal network infrastructure - including database security configurations, server and network hardening, internal firewall and security gateway configurations, and wireless setups where applicable.
3 Remote Access and VPN
VPN configurations, third-party access controls and remote desktop implementations - assessed for least privilege enforcement and authentication weaknesses.
4 Applications and APIs
Web applications and APIs in scope - assessed for authentication weaknesses, injection vulnerabilities, access control flaws and data exposure risks in line with OWASP methodology.
5 Pensions Dashboards Programme Specific
For PDP connections, scope must include any environment where live pension data will be used - external infrastructure, internal systems, applications, APIs and remote access services. CyberLab will help you define this scope clearly before testing begins to avoid gaps in your submission report.
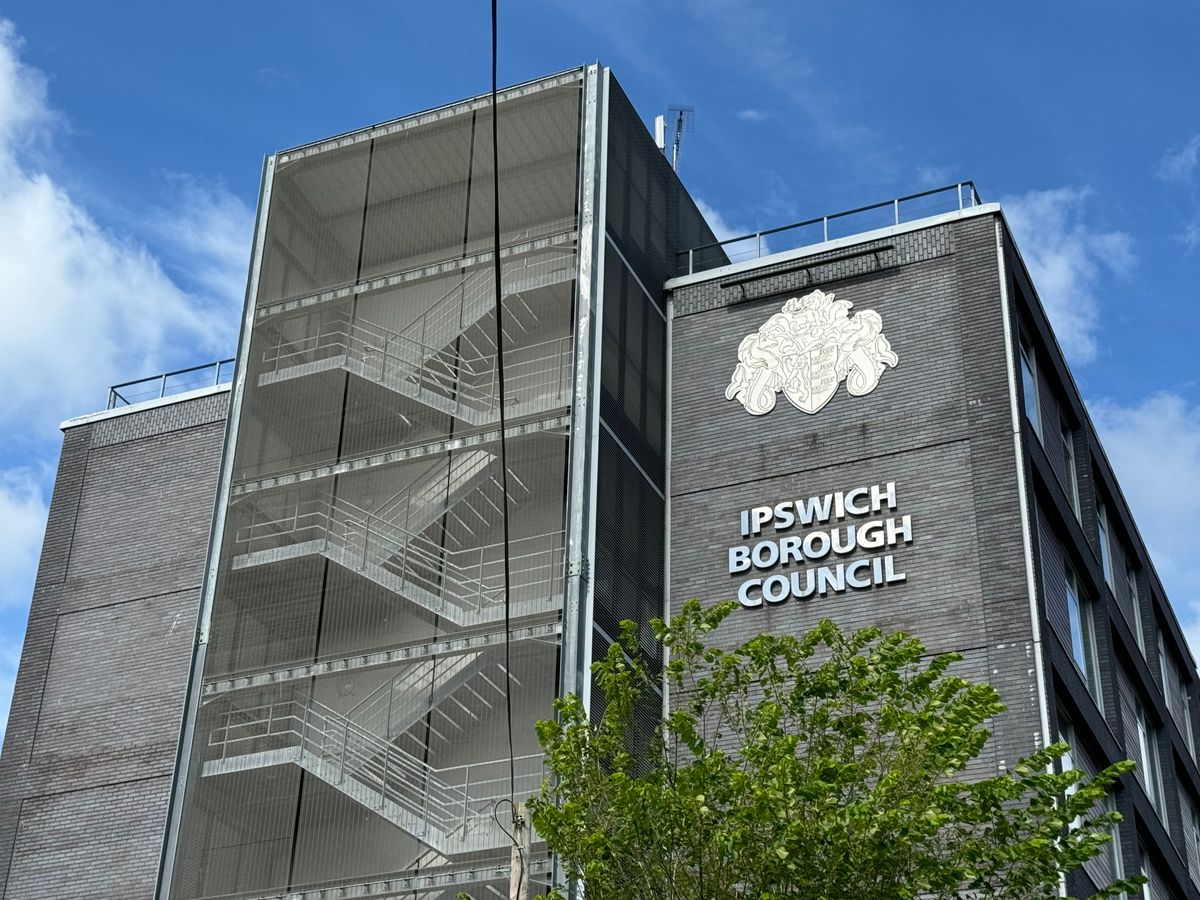
Ipswich Borough Council Maintain PSN Compliance & Accreditation with CyberLab's IT Health Check
IT Health Check Success Story
Ipswich Borough Council
Ipswich Borough Council engaged CyberLab to deliver their annual CHECK-accredited IT Health Check, meeting PSN Code of Connection requirements and maintaining their accreditation year after year. Carried out by SC-cleared CHECK Team Leaders, the assessment covered external and internal infrastructure, vulnerability scanning and access controls – concluding with a clear, audit-ready report to support the council’s PSN submission.
“We’ve worked with CyberLab on our PSN IT Health Check for several years now, and it’s exactly the kind of reliable, consistent service you want for a test like this. Their team understands the specific requirements of local authority testing and PSN accreditation, and the reporting we receive gives us everything we need for our submission without any fuss.”
– Stuart Graham, Cyber Security Manager, Ipswich Borough Council
FAQs:
An IT Health Check is a structured series of controlled security tests used to identify vulnerabilities in an organisation’s IT infrastructure, systems and applications. In the UK public sector, an ITHC is the mandated form of penetration testing required before connecting to approved government networks and data-sharing frameworks. It must be conducted by a CHECK-accredited supplier whose testers are security-cleared.
A standard penetration test can be conducted by any CREST-accredited supplier. An IT Health Check specifically refers to the CHECK-scheme version of penetration testing, which is mandated for public sector use. CHECK-accredited suppliers are security-cleared, making them the only approved option for testing systems that connect to or process government data. CyberLab holds both CHECK and CREST accreditation.
An ITHC is required for any organisation connecting to the Public Services Network (PSN), seeking listing on G-Cloud, achieving NHS Digital Security Protection Toolkit (DSPT) compliance, or connecting to the Pensions Dashboards Programme ecosystem. It is also increasingly required as part of supplier due diligence in regulated industries including financial services, local government and healthcare.
A CyberLab ITHC covers external infrastructure testing, internal infrastructure testing, vulnerability scanning, application and API security assessment, remote access and VPN evaluation, and database security review. The exact scope is defined during the planning phase and agreed with your team to ensure it meets the specific code of connection requirements for your framework – whether that is PSN, G-Cloud, NHS DSPT or the Pensions Dashboards Programme.
A PSN Compliance Test is the specific ITHC process required for PSN connection – it follows the PSN Code of Connection and must be submitted to the PSN Authority for approval. All PSN Compliance Tests are ITHCs, but not all ITHCs are PSN Compliance Tests. CyberLab delivers ITHCs formatted specifically for PSN submission, G-Cloud listing, NHS DSPT compliance and PDP connection – speak with our team to confirm which framework applies to your engagement.
Yes. Organisations connecting to the Pensions Dashboards Programme ecosystem – including pension providers, schemes and integrated service providers – must conduct an ITHC or penetration test and submit a report before connection is approved. The test must comply with the PDP code of connection and be conducted by a CREST or CHECK-accredited supplier. CyberLab is accredited under both schemes.
An ITHC must be conducted by a supplier accredited under the CHECK scheme, administered by the NCSC. CHECK Team Leaders (CTLs) lead the engagement, supported by CHECK Team Members (CTMs). All CHECK-accredited testers hold security clearance. CyberLab’s team includes 7 CHECK Team Leaders and 6 CTMs, all SC or NPPV3-cleared.
Yes. CyberLab has extensive experience working with NHS Trusts and healthcare organisations. Our consultants are SC-cleared and experienced in NHS DSPT requirements. We work with over 60 NHS organisations across the UK.
Timescales vary depending on the size and complexity of your environment. Straightforward ITHCs for smaller organisations can be scoped and delivered within a few weeks. For larger or more complex environments, or where multiple assets are in scope, the process takes longer. CyberLab offers next-day testing for urgent compliance deadlines – speak with our team to discuss your timeline.
Most frameworks that require an ITHC specify that it should be repeated annually, or whenever significant changes are made to in-scope systems or infrastructure. Your CHECK-accredited supplier can advise on the appropriate frequency based on your specific framework requirements.
You receive a comprehensive, audit-ready report detailing all findings, including vulnerability descriptions, CVSS base scores (version 3.0 or above), severity classifications, potential impact assessments and specific remediation guidance for each finding. The report is formatted to meet the submission requirements for PSN, G-Cloud, NHS DSPT and PDP frameworks as applicable.

What is your HackRisk score?
We scan your external attack surface and deliver a board-ready report with your risks and remediation advice, free of charge, within 24 hours.
Dark Web Scanning
Vulnerability Scanning
Recon Scanning
Supply Chain Security
This page was reviewed by Steve Clarke, Head of Penetration Testing at CyberLab, on 11.05.26.
Speak With an Expert
Enter your details and one of our experts will be in touch.
Whether you’re looking to implement basic cyber security best practice, improve your existing defences, or introduce a new system or solution, our team of expert consultants, engineers, and ethical hackers are here to help.
Our team specialise in creating bespoke security solutions and testing packages to improve and maintain your security posture.
We are 100% vendor agnostic and will only ever recommend the best products and solutions for your requirements.