What is NIST CSF 2.0?
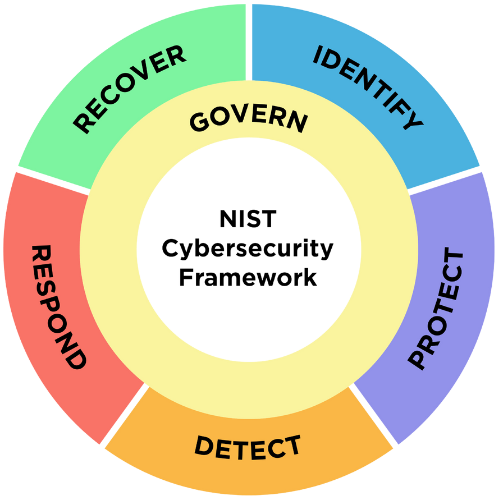
The NIST Cybersecurity Framework (CSF) 2.0 is a voluntary, internationally recognised framework published by the US National Institute of Standards and Technology in February 2024. It gives organisations of any size and sector a common structure for understanding, assessing and reducing cyber security risk, built around six functions: Govern, Identify, Protect, Detect, Respond and Recover.
Version 2.0 added Govern as a new function, putting cyber security strategy, accountability and risk management alongside the technical controls, and widened the scope from critical infrastructure to every type of organisation. The six functions break down into 22 categories and 106 subcategories, and Profiles and Implementation Tiers help you set realistic, staged goals.
NIST CSF is not mandatory in the UK, but many UK organisations use it as a risk-based benchmark that sits alongside ISO 27001, the NCSC Cyber Assessment Framework and Cyber Essentials. It is especially useful where a board wants a clear maturity score, where customers or parent companies are based in the US, or where a team needs a prioritised plan rather than a list of findings.
A CyberLab NIST CSF 2.0 assessment turns the framework into a practical plan. A consultant guides you through the assessment, scores your position across all six functions and builds a staged gap-to-goal plan to fit your risk appetite.
Why Choose CyberLab for a NIST CSF 2.0 Assessment?
CyberLab is trusted by over 1,200 organisations across the UK to secure their operations, systems and data.
NIST CSF 2.0 Assessment: The CyberLab Approach
Our Accreditations
As an ISO 27001 certified consultancy and NCSC Cyber Advisor, trusted by 1,200+ organisations including NHS Trusts, local authorities and financial services firms, we deliver consultant-led NIST CSF 2.0 assessments at a fixed price of £2,499 ex VAT.
Who Needs a NIST CSF 2.0 Assessment?
A NIST CSF 2.0 assessment is a good fit if your organisation:
Has no formal framework in place and wants a structured starting point beyond Cyber Essentials.
–
Is working toward ISO 27001 or reporting against the NCSC Cyber Assessment Framework and wants a baseline first.
–
Has US customers, parent companies or supply chain requirements that reference NIST CSF, NIST SP 800-171 or CMMC.
–
Needs a maturity score and staged plan for the board or leadership team to track.
–
Already uses Sophos tooling and wants to see how well it maps to framework outcomes.
FAQs:
NIST CSF 2.0 is a voluntary cyber security framework published by the US National Institute of Standards and Technology in February 2024. It helps organisations of any size assess and reduce cyber security risk across six functions: Govern, Identify, Protect, Detect, Respond and Recover. It is widely used internationally, including by UK organisations.
The biggest change is a new Govern function, which covers cyber security strategy, roles, accountability and risk management. The framework’s scope also widened from critical infrastructure to all organisations. In total there are six functions, 22 categories and 106 subcategories, with Profiles and Implementation Tiers used to set and track goals.
No. NIST CSF is voluntary and is not a UK legal requirement. UK organisations use it as a risk-based benchmark alongside ISO 27001, the NCSC Cyber Assessment Framework and Cyber Essentials, and it is often referenced by US customers and supply chain partners.
A NIST CSF 2.0 assessment benchmarks your cyber security programme against the framework’s six functions. It produces a score, a view of where you are today (your current profile) and a plan to reach where you want to be (your target profile). CyberLab’s assessment is consultant-led and takes up to two days.
You receive an overall score with a per function breakdown and radar chart, a current and target profile, a gap-to-goal plan built around Implementation Tiers, and Sophos activation mapping. A consultant reviews your answers and books a follow-up call to walk you through the results.
A Profile describes your cyber security outcomes at a point in time: your current Profile shows where you are, and your target Profile shows where you want to be. Implementation Tiers (Partial, Risk Informed, Repeatable and Adaptive) describe how rigorously your organisation manages cyber security risk.
The assessment can take up to two days, depending on the complexity of your organisation.
Yes. A CyberLab Cyber Security Consultant will guide you through the assessment, review your answers and provide an action plan. They will book a follow-up to discuss your results.
The NIST CSF 2.0 Assessment delivered by CyberLab costs £2,499 ex VAT.*
*All terms and conditions apply. Price excludes VAT.
ISO 27001 is a certifiable management system standard, while the NCSC Cyber Assessment Framework is outcome-based guidance for essential services. NIST CSF is a flexible, voluntary framework that scores maturity and sets priorities. Many organisations use it as a baseline before pursuing ISO 27001 or reporting against the CAF, and the three align well.
Activation mapping links the priorities in your gap-to-goal plan to Sophos controls that can help close them. For example, incident mitigation outcomes can map to Sophos MDR, Intercept X and Firewall, and recovery planning can map to Synchronised Security and MDR-led incident response. The assessment itself is independent, and the mapping is there to give you a practical next step.