What is Sophos XDR?
Sophos XDR (extended detection and response) is a security operations solution that collects and correlates activity from across your environment, so your team can find and stop threats that move between systems. It is designed for organisations with their own IT or security team who want to run detection and response in-house.
Sophos XDR Powered by Secureworks is the latest version of Sophos XDR. Following Sophos’s acquisition of Secureworks in 2025, it brings Secureworks’ Taegis detection and response capabilities and Counter Threat Unit intelligence into Sophos XDR, at no change in price for existing customers.
Sophos Endpoint, endpoint detection and response (EDR) and the Sophos Email Monitoring System are included. It connects to over 500 Sophos and third-party tools, including Microsoft, so you can use the security stack you already have.
Sophos XDR is part of Sophos Fusion, the Sophos AI-Native Cybersecurity Defense System and the evolution of Sophos Central. If you would rather Sophos analysts run detection and response for you, the same technology powers the fully managed Sophos MDR service.
Why Choose CyberLab for Sophos XDR?
CyberLab is trusted by over 1,200 organisations across the UK to secure their operations, systems and data.
What Sophos XDR Includes
Sophos XDR Powered by Secureworks combines Sophos’s protection with Secureworks’ security operations heritage, all managed from the new Security Operations area in Sophos Fusion.
How Sophos XDR Works
Sophos XDR uses AI to take the manual effort out of security operations, while your analysts stay in control of every decision.
How CyberLab Delivers Sophos XDR
We make sure Sophos XDR is scoped, deployed and tuned for your environment, then stay with you as your UK partner.
Sophos XDR or Sophos MDR: Which Is Right for You?
Sophos XDR and Sophos MDR run on the same technology. The difference is who does the work: your team, or Sophos analysts on your behalf.
Choose Sophos XDR if you have a security team that wants one place to detect, investigate and respond, with full control over every action.
Choose Sophos MDR if you need round-the-clock cover without hiring a security operations team. Explore Sophos MDR
Not sure? Many organisations start with Sophos XDR and move to Sophos MDR as their needs grow. We will recommend the right option during a free environment review.
Our Sophos Partner Credentials
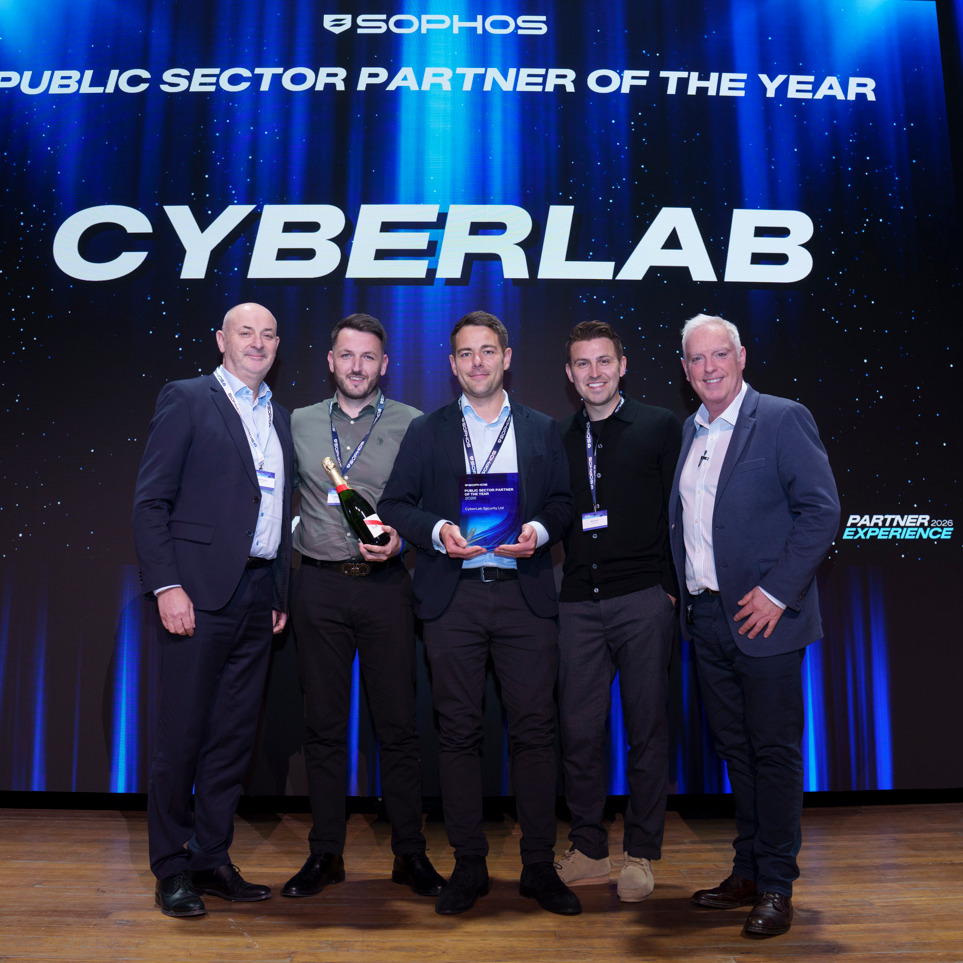
As a Sophos Titanium Partner and Sophos Public Sector Partner of the Year 2026, CyberLab is one of the UK’s leading Sophos MDR delivery partners. Together with Sophos, we protect over 600 organisations, backed by our own CREST, CHECK and ISO-certified security team.
Sophos Titanium Partner

Sophos MDR Partner

Sophos Endpoint Partner

Sophos Firewall Partner

Sophos MSP Partner

Sophos Partner Platform
AWARD
CyberLab Named Sophos Public Sector Partner of the Year 2026 and Awarded Titanium Partner Status
– Chris Bell, Senior Vice President of Global Channel at Sophos
Extend Sophos XDR with Sophos Fusion
Every Sophos product you add gives Sophos XDR more context and more ways to respond, because each one shares data and acts as part of one connected defence.
How Much Does Sophos XDR Cost?
Sophos XDR pricing depends on the size of your environment and what you add to it. The main factors are the number of users and servers covered, the length of your term and any add-ons such as Sophos Next-Gen SIEM or Sophos AI Defense. Sophos Endpoint, EDR and the Email Monitoring System are included, which often replaces tools you pay for separately today. If you already use Sophos, we can review your licences and show you the upgrade path to Sophos XDR. Speak with our team for a tailored quote.
Sophos XDR: Customer Success Stories
Sophos XDR
East Lothian Council
East Lothian Council strengthened 24/7 threat detection and response across a complex local authority estate with Sophos Taegis MDR, built on the Secureworks Taegis technology now integrated into Sophos XDR. CyberLab delivered a rapid proof of concept, full deployment and ongoing public sector support, giving the council faster response and predictable long-term costs.
Sophos XDR
Buckinghamshire Council
A Sophos customer through CyberLab since 2005, Buckinghamshire Council has moved its schools from Sophos Enterprise to Sophos Central and Intercept X Advanced, the same Sophos Endpoint protection now included with Sophos XDR. Our consultative approach helped the council secure just over 40,000 licences within the budget originally planned for 30,000.
REPORT
Sophos State of Ransomware Report 2026
Annual Report on Global Ransomware Trends
What You Get
From Sophos
- Sophos Endpoint, EDR and the Email Monitoring System included
- Thousands of Secureworks detections, plus your own custom rules
- AI-assisted cases, summaries and plain-English search
- 130+ SOAR playbooks and 500+ integrations
- Sophos X-Ops and Counter Threat Unit threat intelligence
From CyberLab
- Scoping, deployment and configuration by Sophos-certified engineers
- Integration of your Microsoft and third-party tools
- Help enabling detections, custom rules and automations
- Regular health checks and a dedicated UK account manager
- Managed Security Support for hands-on help
- A simple path to Sophos MDR or Next-Gen SIEM when you need it
Sophos XDR on the Tales from the CyberLab Podcast
TALES FROM THE CYBERLAB
Episode 25 | Agentic AI in Cyber Security Explained with Sophos
with Dave Mareels, VP of Product Management at Sophos
Webinar Series
Sophos MDR Quarterly Updates
Adam Myers, Sales Director at CyberLab, teams up with experts from Sophos to explore the forefront of proactive cyber defences. Each session delivers essential updates, compelling real-world success stories, and practical strategies to enhance your organisation’s security posture.
FAQs:
Extended detection and response (XDR) is a security approach that brings together detection, investigation and response across endpoints, identity, email, cloud, network and third-party tools in one place. Instead of investigating alerts in separate consoles, your team sees connected activity as a single case, which makes multi-stage attacks easier to spot and stop.
Sophos XDR Powered by Secureworks is the latest version of Sophos XDR. It brings Secureworks’ Taegis detection and response capabilities, thousands of additional detections and Counter Threat Unit intelligence into Sophos XDR, following Sophos’s acquisition of Secureworks in 2025. It is managed from the Security Operations area of Sophos Fusion.
Not exactly. Sophos XDR Powered by Secureworks takes the best of Taegis, including its detections, automation and threat intelligence, and builds it into Sophos XDR within Sophos Fusion. Sophos continues to support existing Taegis platform customers. If you use Taegis today, speak with our team about the right path for your organisation.
Existing Sophos XDR customers get the upgraded capabilities with no change in price. These include the new Security Operations interface, thousands of additional detections, a custom rule builder, expanded two-way integrations, SOAR automation, integrated threat intelligence and the Sophos Email Monitoring System.
Sophos XDR is the technology your own team uses to detect, investigate and respond to threats. Sophos MDR is a fully managed service in which Sophos analysts use the same technology to do that work for you, 24/7. Choose Sophos XDR if you have an in-house security team, or Sophos MDR if you need round-the-clock cover without building one.
Yes. Sophos Endpoint and Sophos EDR are included with Sophos XDR, along with the Sophos Email Monitoring System. Built-in prevention stops more threats upfront, so your team has fewer alerts to investigate.
Yes. Sophos XDR is vendor-agnostic and supports over 500 integrations across endpoint, identity, email, cloud, network and business applications, including extensive Microsoft integration. Two-way integrations let your team take response actions directly in supported third-party tools, and CyberLab configures these for you during deployment.
Yes. Sophos XDR and Sophos MDR run on the same technology within Sophos Fusion, so moving to fully managed detection and response does not require a new deployment. CyberLab can help you decide when the switch makes sense.
XDR is built for real-time detection, investigation and response. A traditional SIEM focuses on collecting and storing logs for investigations and compliance. Sophos Next-Gen SIEM is an optional add-on that extends Sophos XDR with long-term retention of up to 10 years and compliance reporting, so you do not need to run a separate SIEM.
AI is part of the core of Sophos XDR. It correlates signals, groups related activity into prioritised cases, writes case summaries and lets analysts search data in plain English. Your team stays in control of every response decision.