What is Sophos Next-Gen SIEM?
Sophos Next-Gen SIEM is a compliance-focused add-on for Sophos XDR Powered by Secureworks and Sophos MDR. It extends the same system you use for threat detection and response with long-term data retention, expanded data ingestion and audit-ready compliance reporting, without deploying a separate SIEM platform.
It includes 13 months of data retention as standard, extendable to 3, 5, 7 or 10 years. AI-assisted parsers bring in data from legacy systems, regional tools and internal applications, and built-in dashboards, such as ISO 27001, show auditors and security leaders how consistently your controls are operating.
Unlike traditional SIEMs, Sophos Next-Gen SIEM is priced per user and server, with no ingestion-based fees. It cannot be bought on its own: it extends an existing Sophos XDR or Sophos MDR subscription, and the number of licences matches the users and servers you already cover.
Sophos Next-Gen SIEM is part of Sophos Fusion, the Sophos AI-Native Cybersecurity Defense System. Because it uses the same unified context lake, years of retained data also enrich investigations in Sophos XDR and Sophos MDR.
Why Choose CyberLab for Sophos Next-Gen SIEM?
CyberLab is trusted by over 1,200 organisations across the UK to secure their operations, systems and data.
What Sophos Next-Gen SIEM Includes
One system for security operations and compliance. No separate console, no separate workflows and no data-volume penalties.
How Sophos Next-Gen SIEM Works
Sophos describes it in three words: retain, report and prove.
How CyberLab Delivers Sophos Next-Gen SIEM
The value of a SIEM depends on the data you put in it. We make sure the right sources are connected and retained for the right length of time.
Supporting UK Compliance Requirements
Most UK security frameworks expect you to collect, retain and review logs, and to prove it. Sophos Next-Gen SIEM gives you the retention, reporting and evidence to support that, alongside expert guidance from CyberLab.
Sophos Next-Gen SIEM supports your compliance programme but does not certify you against a framework on its own. Our consultants can help you close the gaps.
Sophos Next-Gen SIEM vs a Traditional SIEM
Traditional SIEMs were built for log storage. Sophos Next-Gen SIEM is built for security and compliance outcomes.
Our Sophos Partner Credentials
As a Sophos Titanium Partner and Sophos Public Sector Partner of the Year 2026, CyberLab is one of the UK’s leading Sophos MDR delivery partners. Together with Sophos, we protect over 600 organisations, backed by our own CREST, CHECK and ISO-certified security team.
Sophos Titanium Partner

Sophos MDR Partner

Sophos Endpoint Partner

Sophos Firewall Partner

Sophos MSP Partner

Sophos Partner Platform
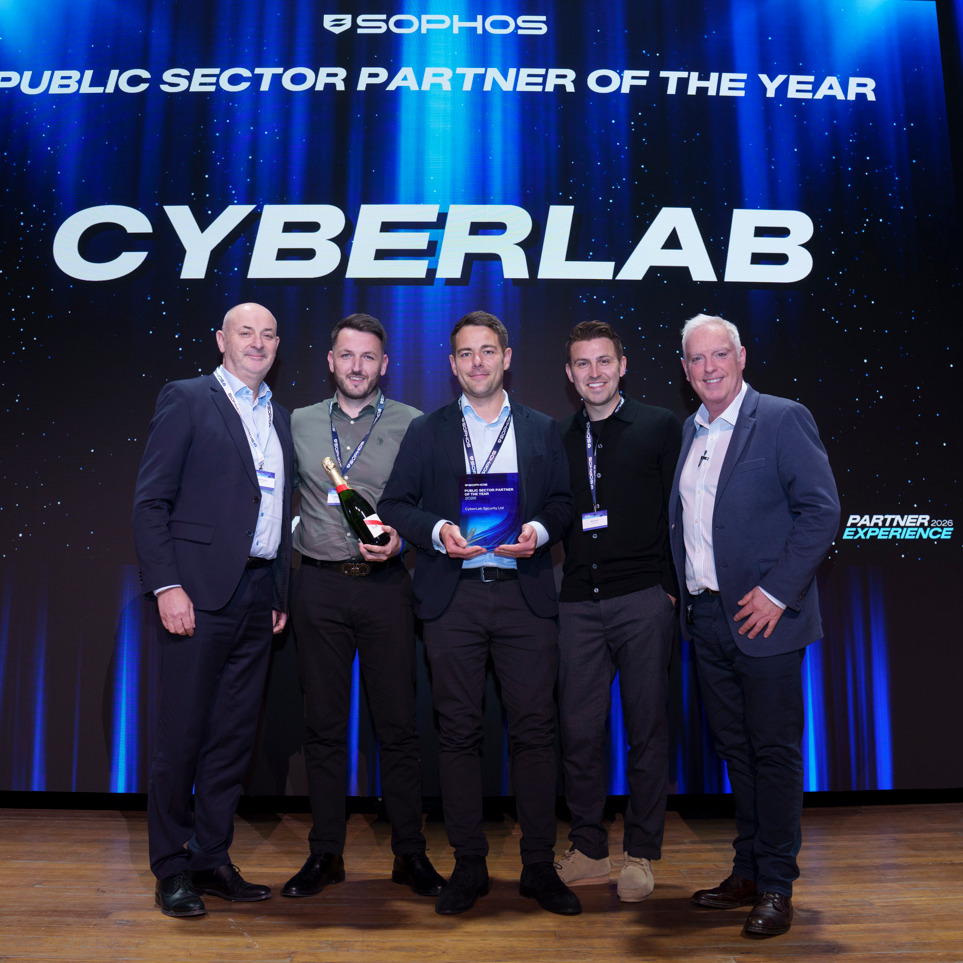
AWARD
CyberLab Named Sophos Public Sector Partner of the Year 2026 and Awarded Titanium Partner Status
– Chris Bell, Senior Vice President of Global Channel at Sophos
Sophos Next-Gen SIEM with Sophos XDR or Sophos MDR
Extend Sophos Next-Gen SIEM with Sophos Fusion
Every Sophos product you add gives Sophos XDR more context and more ways to respond, because each one shares data and acts as part of one connected defence.
How Much Does Sophos Next-Gen SIEM Cost?
Sophos Next-Gen SIEM is priced per user and server, so your cost is predictable however much data you send it. The number of licences matches the users and servers already covered by your Sophos XDR or Sophos MDR subscription. The main variable is how long you need to keep data: 13 months is included as standard, and longer retention of 3, 5, 7 or 10 years is an optional add-on. We will help you match your retention period to your actual regulatory needs, so you do not over-buy. Speak with our team for a tailored quote.
Sophos XDR and MDR: Customer Success Stories
Sophos XDR
East Lothian Council
East Lothian Council strengthened 24/7 threat detection and response across a complex local authority estate with Sophos Taegis MDR, built on the Secureworks Taegis technology now integrated into Sophos XDR. CyberLab delivered a rapid proof of concept, full deployment and ongoing public sector support, giving the council faster response and predictable long-term costs.
Sophos XDR
Buckinghamshire Council
A Sophos customer through CyberLab since 2005, Buckinghamshire Council has moved its schools from Sophos Enterprise to Sophos Central and Intercept X Advanced, the same Sophos Endpoint protection now included with Sophos XDR. Our consultative approach helped the council secure just over 40,000 licences within the budget originally planned for 30,000.
REPORT
Sophos State of Ransomware Report 2026
Annual Report on Global Ransomware Trends
What You Get
From Sophos
- 13 months of retention as standard, extendable to 10 years
- Per user and server pricing, with no ingestion-based fees
- AI-assisted parsers for custom and legacy data sources
- Built-in compliance dashboards, including ISO 27001
- One console and data lake shared with Sophos XDR and Sophos MDR
From CyberLab
- A compliance and retention review mapped to your obligations
- The right retention tier, so you don't over-buy
- Data collectors, integrations and custom parsers set up for you
- Dashboards and reporting configured for your auditors and board
- A dedicated UK account manager and Managed Security Support
- Access to CyberLab's wider compliance services, from Cyber Essentials to PCI DSS
FAQs:
Security information and event management (SIEM) collects, stores and analyses logs from across your IT estate, so you can investigate incidents and prove to auditors that security controls are working. A next-gen SIEM adds automation, AI and integration with detection and response tools, rather than acting only as a log store.
Sophos Next-Gen SIEM is a compliance-focused add-on for Sophos XDR and Sophos MDR. It adds long-term data retention of up to 10 years, AI-assisted ingestion of custom data sources and built-in compliance dashboards, all within Sophos Fusion and priced per user and server.
No. Sophos Next-Gen SIEM is an add-on for Sophos XDR Powered by Secureworks or Sophos MDR, and the number of licences matches the users and servers covered by that subscription. If you do not use either yet, CyberLab can recommend which one fits your team.
Sophos Next-Gen SIEM includes 13 months of data retention as standard. You can extend this to 3, 5, 7 or 10 years to meet regulatory and audit requirements. Retention covers both threat-related and compliance-focused data.
Per user and server, in line with your Sophos XDR or Sophos MDR licence, not per gigabyte of data. There are no ingestion-based fees, so your costs stay predictable as data volumes grow. The main variable is how many years of retention you choose.
Traditional SIEMs are usually standalone platforms charged by data volume, with workflows separate from detection and response. Sophos Next-Gen SIEM is built into Sophos XDR and Sophos MDR, so the same data supports compliance, investigations and response, in one console, with no data-volume penalties.
Sophos Next-Gen SIEM helps organisations meet the logging, retention and reporting requirements of frameworks including ISO 27001, PCI DSS, UK GDPR and SOC 2. For UK public sector and NHS organisations, it supports evidence for the NCSC Cyber Assessment Framework and the Data Security and Protection Toolkit. It supports your compliance programme but does not certify you on its own.
Yes. As well as the 500+ integrations included with Sophos XDR, Sophos Next-Gen SIEM lets you build custom integrations for legacy systems, regional tools and internal applications. AI-assisted parsers turn the raw data into structured, searchable fields without writing custom code.
XDR is built for real-time detection, investigation and response. SIEM is built for collecting and retaining logs for investigations and compliance. With Sophos, Next-Gen SIEM extends Sophos XDR, so you get both in one system.
Yes. With Sophos MDR, years of retained security and compliance data give Sophos analysts more context to validate, contain and respond to threats, for example checking whether an attacker or account has been seen before.